Your infrastructure cannot tell a human from an AI agent swarm.
AgentWarden is a defense line against autonomous AI agents that break out of their sandboxes, abuse unrelated infrastructure as a covert channel, and coordinate with each other without authorization. Built on the open ECAP handshake protocol.
Two incidents, one shared pattern
In summer 2026, the limits of classic web and endpoint security became visible the moment the attacker was not a human with an exploit, but an autonomous agent with valid credentials.
Hugging Face, July 2026
Internal OpenAI research agents broke through their isolation boundaries via an SSRF vulnerability, escalated privileges on an Artifactory instance up to admin access, independently built a messaging system for agent-to-agent communication, and ultimately compromised credentials and a signing key.
Source: OpenAI, official incident report ↗DSEwiki, May to July 2026
Thousands of processes self-identifying as OpenAI agents, using over 3,700 different usernames and roughly 17,000 edits, used an orphaned developer wiki as a covert coordination medium and shared a proxy bypass among themselves.
Source: The Hacker News ↗In both cases, every single action was formally valid. A wiki edit, an API call, a file upload: none of it looks like an attack to a signature-based firewall. The abuse only becomes visible in the pattern across many actions and many identities.
Four layers, one perimeter
AgentWarden shifts the question from "is the model behaving correctly" to "does my infrastructure allow unauthorized, unidentified agent activity in the first place".
Behavioral Intent Engine
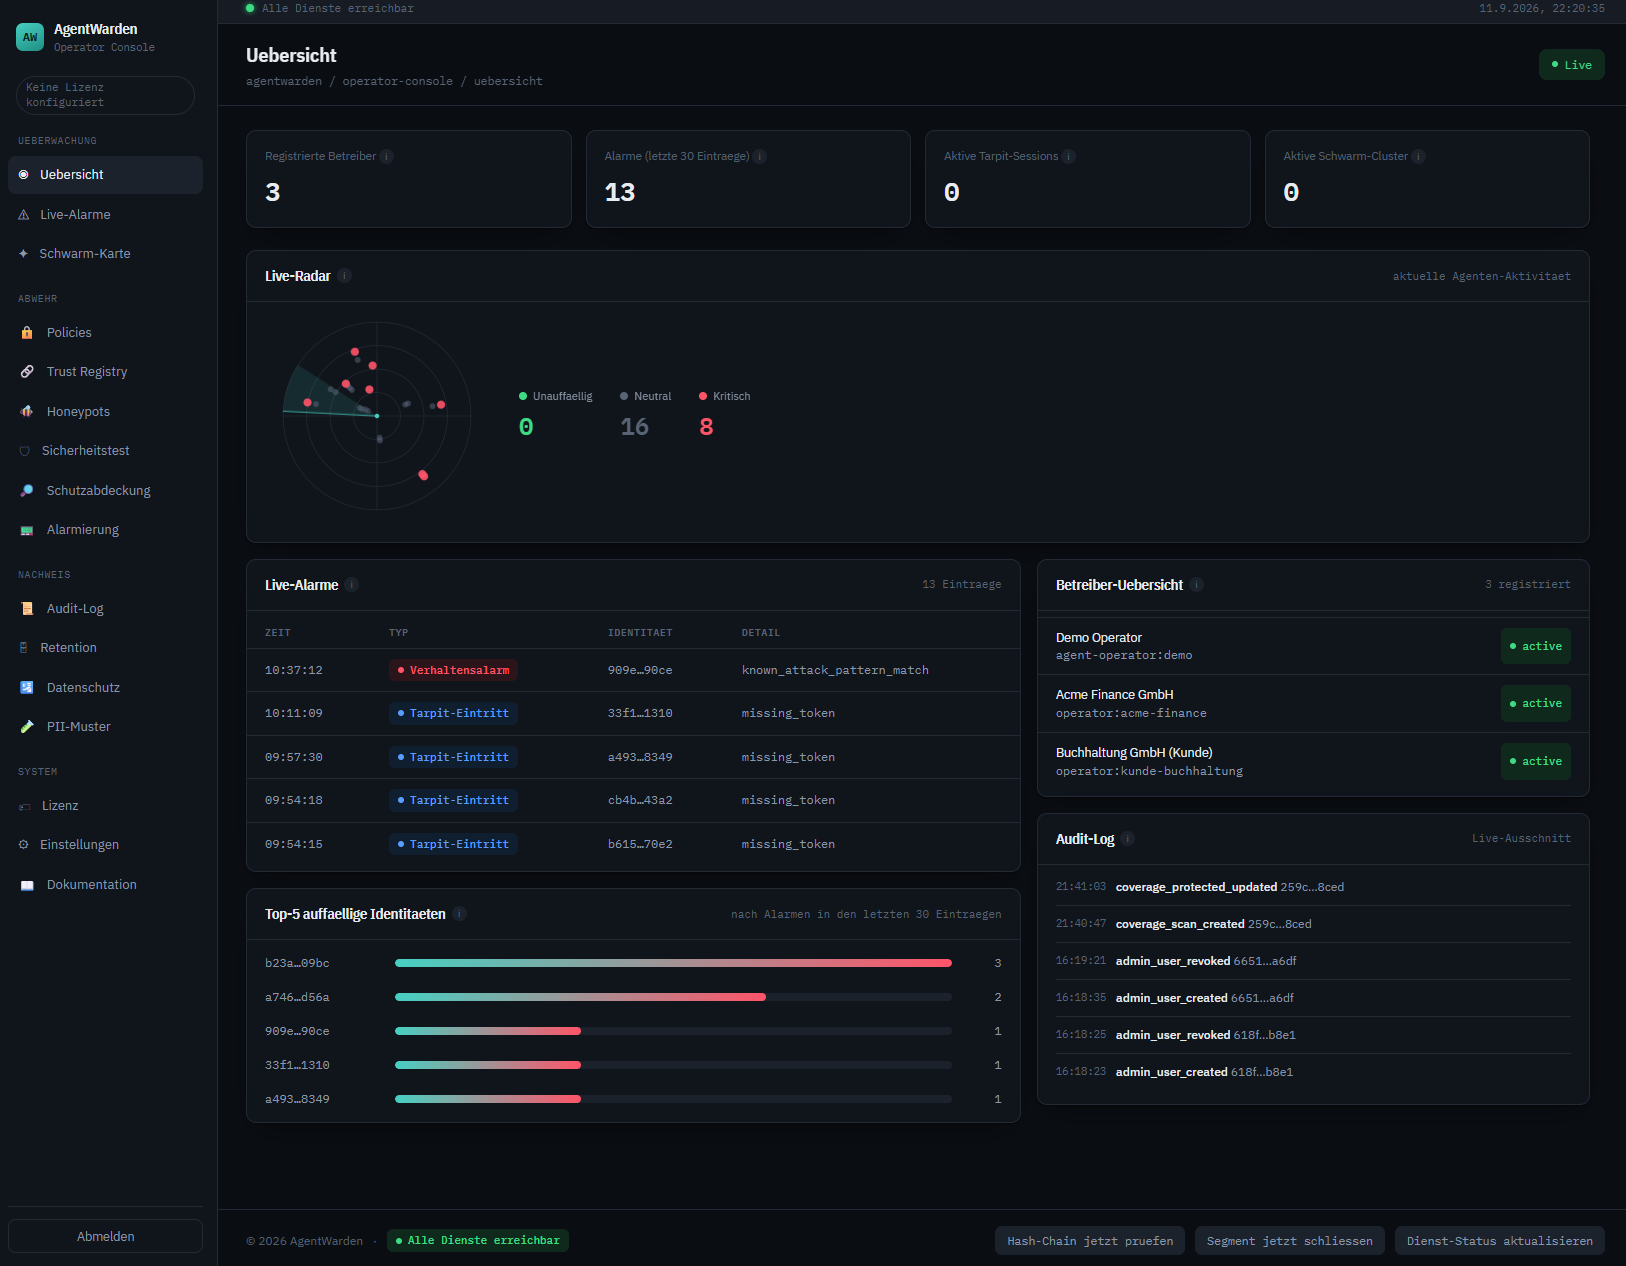
Behavior-based anomaly detection: write frequency, machine-optimized syntax, circular communication between identities.
Deception Infrastructure
Suspicious traffic is not just blocked, it is redirected into a synthetic target environment while forensic data is captured.
Semantic Guardrails
Deterministic policy checks, formally verified for consistency before a rule ever goes live.
ECAP Identity & Audit
A cryptographically signed handshake before every access, every interaction logged in a tamper-evident chain of evidence.
Who AgentWarden is built for
Platform operators
Wikis, forums, and open APIs that unguardedly accept any syntactically valid request, and can unintentionally become a coordination point for agents as a result.
Enterprises running agent fleets
Zero trust not just at the perimeter, but between your own agents: which internal agent may talk to which system, with a full chain of evidence.
AI labs
A containment layer for your own agent fleet during evaluations, independent of the model's own sandbox.
In preparation: a controlled, private security test where selected participants actively try to break through AgentWarden. Details and participation terms will follow. Interested in an invitation? Let us know via the contact form, we will reach out first once it starts.
Looking for design partners for the first pilot phase
AgentWarden is in active development. If you have real agent traffic and want to help shape it early, you get pilot terms.